Security
Digital Signage Security You Can Check for Yourself
If you're reviewing firmChannel's digital signage security for your organization or a client, here is how the platform is audited, hosted and run, and the reports to check it against.
SOC 2 Type II audited · Annual third-party penetration test · Hosted in Canada and the US · A private database for every customer · Passkey sign-in
Digital signage security, independently audited
firmChannel is independently audited to SOC 2 Type II under the Security criteria. The latest report carries an unqualified opinion, with no exceptions noted, and we send the full report to your team under NDA.
An independent third-party firm also tests the platform once a year. The latest penetration test found no Critical or High issues, and we'll share the full report rather than a summary letter.
How each customer is kept apart
Every customer on firmChannel is its own enterprise, with a dedicated instance and its own private database. Customers never share a database.
Each enterprise also has its own sign-in. That's deliberate: if a set of credentials ever leaks, it reaches one organization and nothing else. It's also why there's no single login that spans several clients.
Data residency: where your data lives
firmChannel runs on AWS in Canada and the US. If you're in Canada, your data is hosted in Canada. If you're in the US, it's hosted in the US. Either way, you can meet your data-residency requirements without a special arrangement.
Sign-in and access
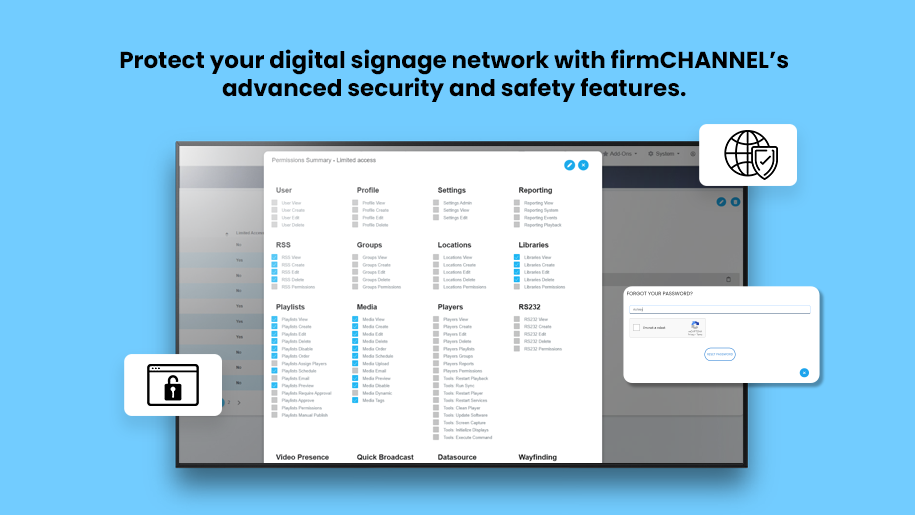
These controls are built into the software itself. Our Security & Safety page, under Software, shows how each one works.
- Single sign-on with your identity provider, on the Enterprise edition
- Multi-factor authentication with passkeys or authenticator apps
- Configurable password policies, with password history
- Automatic lockout of accounts left inactive for 90 days
- Roles and permissions that decide who can publish, schedule, manage players or send display commands, down to individual RS-232 controls
Encryption
Data at rest is encrypted with AES-256, using keys managed by AWS, and backups are encrypted with keys in AWS Key Management Service. Data in transit is protected with TLS 1.2 or higher. Databases are encrypted from launch, and our policy is that nothing is stored unencrypted on persistent media. More on encryption.
How we run the platform
Perimeter
A web application firewall in front of the platform
Threat detection
Continuous threat detection on our AWS accounts and servers
Vulnerability scanning
Monthly infrastructure scans, plus weekly malware scans
Patching
Critical and High operating system security updates installed automatically every night
Code security
Automated code scanning on every pull request, and review by someone other than the author before code merges
Fix times
Critical vulnerabilities found by our scanning are fixed within 72 hours or contained with compensating controls, and High within 14 days
Administrative access
Multi-factor authentication on all production and cloud console access
Secrets
Short-lived IAM role credentials for AWS access, other API keys held in AWS Secrets Manager, and no keys or secrets in code
Logging
Detailed activity logs, with AI actions attributed to the person who requested them (Enterprise edition); security event logs kept for a year; logs provided on request for your SIEM
Incident handling
Documented incident response and data breach response policies
Insurance
Corum carries cyber liability insurance
Backup, recovery and resilience
- Encrypted backups: seven daily, five weekly and eighteen monthly copies of each database
- Restore tests every quarter, and a disaster recovery exercise every year
- A 24-hour recovery point objective
- If the platform can't be reached, players keep showing their cached content, so your screens don't go dark
AI, under your control
firmChannel's AI features are on the Enterprise edition only, and an administrator can switch every one of them off, before deployment if you prefer. Customer data isn't used to train AI models.
AI features rely on third-party providers. If your policy requires all processing to stay in your own country, or rules out generative AI entirely, switch AI off and the rest of the platform works as normal.
For partners and managed service providers
Resell firmChannel, or run it for your clients? Bring us their security review. We've filled in vendor questionnaires for hospitals, banks and public agencies, and we'll work through your client's with you. We'll also send the SOC 2 Type II report under NDA and the full pen test report straight to your client's IT team.
- Our SOC 2 Type II report, under NDA
- The full report from our latest annual penetration test
- Answers to your vendor security questionnaire
- A call with our pre-sales team on hosting, architecture and recovery
FAQ
Questions security teams ask
Is firmChannel SOC 2 audited?
Yes. firmChannel is independently audited to SOC 2 Type II under the Security criteria, with no exceptions noted. We send the report under NDA.
Is SOC 2 a certification?
No. SOC 2 is an audit report issued by an independent firm. firmChannel's latest SOC 2 Type II report has no exceptions noted, and we send it under NDA.
How often is the platform penetration tested?
Once a year, by an independent third-party firm. The latest test found no Critical or High issues.
Where is our data hosted?
On AWS. Canadian customers' data is hosted in Canada, and US customers' data in the US.
Can another customer ever see our data?
No. Each customer is its own enterprise, with a dedicated instance, a private database and its own sign-in.
How quickly do you fix vulnerabilities?
Critical vulnerabilities from our scanning are fixed within 72 hours, or contained with compensating controls until they are, and High within 14 days.
What happens to our screens if the platform goes down?
They keep playing their cached content until the connection returns.
Can we turn AI off?
Yes. An administrator can switch off every AI feature, and AI is only available on the Enterprise edition.
Do you support single sign-on?
Yes, on the Enterprise edition, along with multi-factor authentication using passkeys or authenticator apps.
Get the reports
Tell us who should receive the reports. We'll send them, and our pre-sales team can take your security team through the rest of their list.